SC-100 Exam Dumps - Microsoft Cybersecurity Architect
Searching for workable clues to ace the Microsoft SC-100 Exam? You’re on the right place! ExamCert has realistic, trusted and authentic exam prep tools to help you achieve your desired credential. ExamCert’s SC-100 PDF Study Guide, Testing Engine and Exam Dumps follow a reliable exam preparation strategy, providing you the most relevant and updated study material that is crafted in an easy to learn format of questions and answers. ExamCert’s study tools aim at simplifying all complex and confusing concepts of the exam and introduce you to the real exam scenario and practice it with the help of its testing engine and real exam dumps
Your company finalizes the adoption of Azure and is implementing Microsoft Defender for Cloud.
You receive the following recommendations in Defender for Cloud
• Access to storage accounts with firewall and virtual network configurations should be restricted,
• Storage accounts should restrict network access using virtual network rules.
• Storage account should use a private link connection.
• Storage account public access should be disallowed.
You need to recommend a service to mitigate identified risks that relate to the recommendations. What should you recommend?
Your network contains an Active Directory Domain Services (AD DS) domain named Domain1.
You have a Microsoft Entra tenant.
Domain1 syncs with the tenant by using Microsoft Entra Connect.
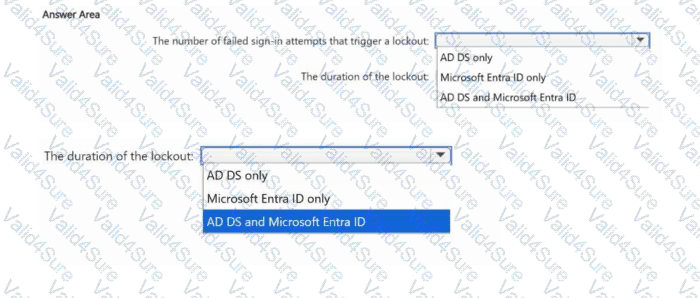
You need to evaluate Microsoft Entra smart lockout by testing the following account lockout considerations:
The number of failed sign-in attempts that trigger a lockout.
Azure subscription that uses Azure Storage.
The company plans to share specific blobs with vendors. You need to recommend a solution to provide the vendors with secure access to specific blobs without exposing the blobs publicly. The access must be t\me-Vim\ted. What should you include in the recommendation?
You have an Azure subscription.
You have an on-premises datacenter that contains Microsoft SQL Server instances. Each instance contains multiple databases.
You have a Microsoft 365 subscription.
You plan to implement a solution to scan the databases for vulnerabilities that compromise data security.
You need to recommend what to configure before the databases can be scanned.
What should you recommend?
You have an Azure subscription that contains several storage accounts. The storage accounts are accessed by legacy applications that are authenticated by using access keys.
You need to recommend a solution to prevent new applications from obtaining the access keys of the storage accounts. The solution must minimize the impact on the legacy applications.
What should you include in the recommendation?
Your company has an on-premises network, an Azure subscription, and a Microsoft 365 E5 subscription. The company uses the following devices:
• Computers that run either Windows 10 or Windows 11
• Tablets and phones that run either Android or iOS
You need to recommend a solution to classify and encrypt sensitive Microsoft Office 365 data regardless of where the data is stored. What should you include in the recommendation?
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains a Microsoft Sentinel workspace. Microsoft Sentinel data connectors are configured for Microsoft 365, Microsoft 365 Defender, Defender for Cloud, and Azure.
You plan to deploy Azure virtual machines that will run Windows Server.
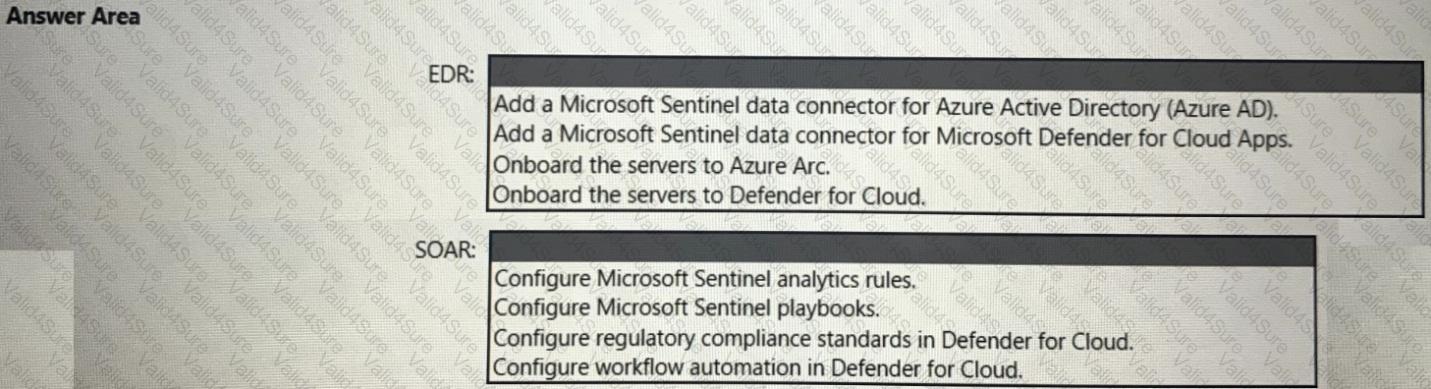
You need to enable extended detection and response (EDR) and security orchestration, automation, and response (SOAR) capabilities for Microsoft Sentinel.
How should you recommend enabling each capability? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

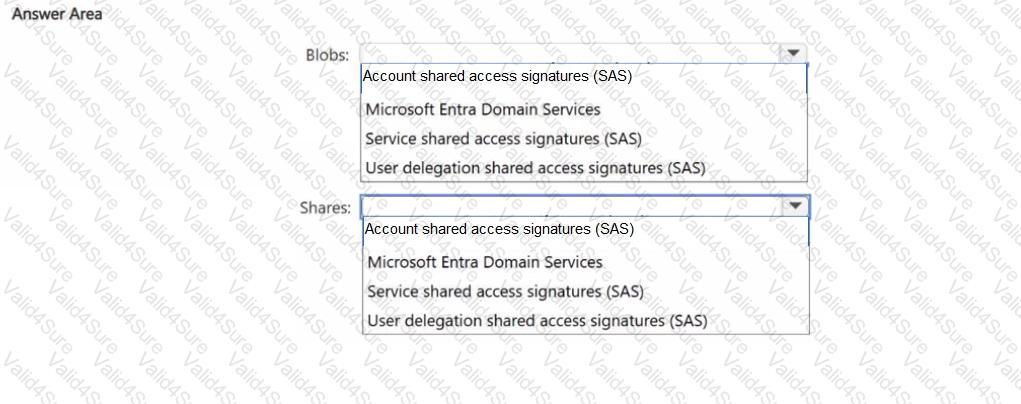
You have an Azure subscription that contains multiple Azure Storage blobs and Azure Files shares.
You need to recommend a security solution for authorizing access to the blobs and shares. The solution must meet the following requirements:
• Support access to the shares by using the SMB protocol.
• Limit access to the blobs to specific periods of time.
• Include authentication support when possible.
What should you recommend for each resource? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.